Information security management system

Information security management system
Informasjonssikkerhet

Certain QMS is a fully-featured quality management system with functionality for management processes, documentation, risk assessment, audit and more. The system also meets the requirements for an organisation-wide information security management system (ISMS).

This means that organisations can use Certain QMS to establish, follow up and document information security in a structured and transparent manner, without additional software or separate ISMS tools.

This article explains how you can use Certain QMS to establish and manage a complete ISMS. We walk through the relevant features of the system and describe what is included in terms of ready-made templates, supporting documentation and tools in our ISMS package.

Certain QMS: a comprehensive ISMS tool

Certain QMS supports the entire lifecycle of information security work, from establishment through to continual improvement, and is suited both to organisations seeking ISO 27001 certification and to those wanting a structured ISMS without formal certification.

The system gives you the tools you need to:

  • Establish an ISMS: Access ready-made procedures, policies and process models that can be adapted to your organisation.
  • Plan and follow up: Use the annual planner functionality to plan activities and tasks, assign responsibilities and ensure that tasks are completed and documented.
  • Assess risk: The risk module provides an overview and control, making it straightforward to follow up on actions.
  • Manage data protection: The DPIA process supports the assessment of high-risk processing activities, and is linked to risk assessment and actions.
  • Ensure compliance: The compliance module helps you document that requirements from legislation, standards and customers are being met.
  • Document processing activities: The records of processing activities provide an overview of the organisation’s personal data processing, functioning as an integrated part of the ISMS.

What is an ISMS?

An information security management system (ISMS) is a framework that helps organisations protect information systematically. It provides structure for how risks are identified, controls are put in place, security measures are documented and follow-up is carried out over time.

The main objectives of an ISMS:

  • Information should always be confidential, accurate and available to those who need it
  • Compliance with legal requirements, standards and internal guidelines

In the same way as a quality management system (QMS), an ISMS combines processes, routines, policies and documentation to give the organisation a clear framework.

An ISMS makes it possible to:

  • Assess and manage risks relating to information
  • Ensure that actions are followed up and documented
  • Clarify roles and responsibilities for security
  • Document compliance with standards and legal requirements
  • Continually improve information security

By using Certain QMS as an ISMS, the organisation has all the necessary tools in one place — from document control and risk assessment to checklists, processes and audit — making implementation and follow-up clear and cohesive.

Why is an ISMS important for the organisation?

An ISMS gives management a systematic framework for documenting and following up that the organisation complies with legislation, regulations and both internal and external requirements relating to information security and data protection.

The main reasons for having an ISMS:

  • Legislation and regulation: An ISMS makes it possible to document that the organisation complies with applicable laws and regulations, such as the Personal Data Act / GDPR and the NIS2 Directive for critical infrastructure, or sector-specific requirements.
  • Standards and certifications: ISO 27001 and other international standards set requirements for the management of information security, and an ISMS provides a documented basis for compliance and any certifications.
  • Customer expectations: More customers require their suppliers to manage information security systematically, and an ISMS provides documentation of this.
  • Risk and vulnerability management: The system makes it possible to identify and manage risks relating to information, whilst follow-up and control are documented.
  • Continual improvement: By establishing a systematic framework, the organisation can follow up on actions, document results and continuously improve its security level.

With an ISMS, organisations can demonstrate to both regulators and customers that they take information security seriously.

A process-oriented approach to ISMS

Certain QMS supports a process-oriented approach to management, meaning that information security work is organised around processes rather than functions or departments.

Information security work is established as a dedicated process area in which both main processes and sub-processes are modelled. This makes it easier to see the full picture of the work and where responsibility lies.

Documentation linked to processes

All documentation (procedures, guides, instructions, templates and more) is linked to the relevant activities in the process, and is also logically organised within a dedicated folder area for information security. Users can navigate via the processes or the folder structure.

All documents have full version control, and both documents and processes can be managed with role-based access, so that only authorised users see relevant content.

Annual planner for information security work

Certain QMS supports a process-oriented approach to management, meaning that information security work is organised around processes rather than functions or departments.

Information security work is established as a dedicated process area in which both main processes and sub-processes are modelled. This makes it easier to see the full picture of the work and where responsibility lies.

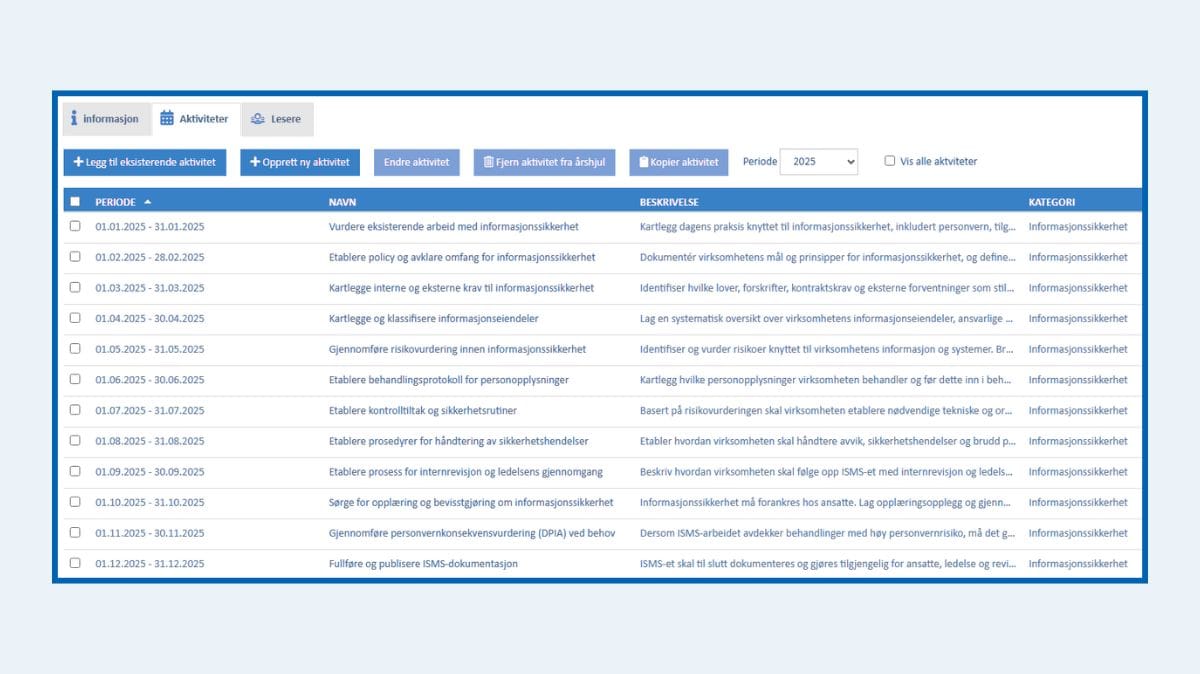
Annual planner for ISMS establishment

The annual planner for ISMS establishment helps you carry out the initial setup work in a structured manner, ensuring that the ISMS is established correctly from the outset.

Contents:

  • 12-month structured plan
  • Activities with clear guidance text and tasks
  • Green status shown when tasks are completed

Examples of activities throughout the year:

  • January: Map existing security work
  • May: Carry out risk assessment
  • July: Establish controls and security routines
  • December: Complete and publish the ISMS
Årshjul etablering av ISMS Certain QMS

Annual planner for ISMS establishment.

Annual planner for continual improvement

Once the ISMS has been established, the system must be kept active. This annual planner provides a template for annual maintenance, follow-up and improvement.

Activities include:

  • Revision of previous risk assessments
  • Internal audit and management review
  • Training and awareness-raising
  • Review of the records of processing activities and DPIA requirements

Ready-made document templates for ISMS

Certain QMS can be delivered with a complete template set for ISMS, giving the organisation a solid starting point for documenting and following up on information security.

The templates are designed to be adapted to the individual organisation, whilst ensuring that all necessary elements are in place.

The template set covers:

  • ISMS policy
  • All necessary procedures, including incident management, access control and operations
  • DPIA procedure and templates
  • Audit plan and audit report
  • Management review

The document templates include:

  • Field lists with guidance text to assist the user
  • Established content templates that can be inserted into documents where relevant

DPIA support in Certain QMS

A DPIA (Data Protection Impact Assessment) is an assessment of how a personal data processing activity may affect individuals’ rights and freedoms. Carrying out a DPIA is required when processing is likely to result in a high risk to data subjects.

Certain QMS supports the entire DPIA process by combining checklists, document templates and risk assessment.

How the system supports DPIA work:

  • Checklist for assessing the need for a DPIA
  • Guidance for assessment in line with the Norwegian Data Protection Authority
  • Risk analysis template for carrying out a DPIA
  • Request function for risk analysis
  • Incident register for data protection risk
  • Dedicated impact areas for data protection rights, confidentiality, availability, integrity, reputation, legal requirements and regulations

Risk analysis request

In Certain QMS, users can submit a request for a risk analysis directly within the system. This enables the data protection officer, information security officer or other relevant roles to receive notification that an analysis of a system or process needs to be carried out.

The feature ensures clear accountability and efficient follow-up, without requiring everyone involved in DPIA or process work to carry out the analysis themselves.

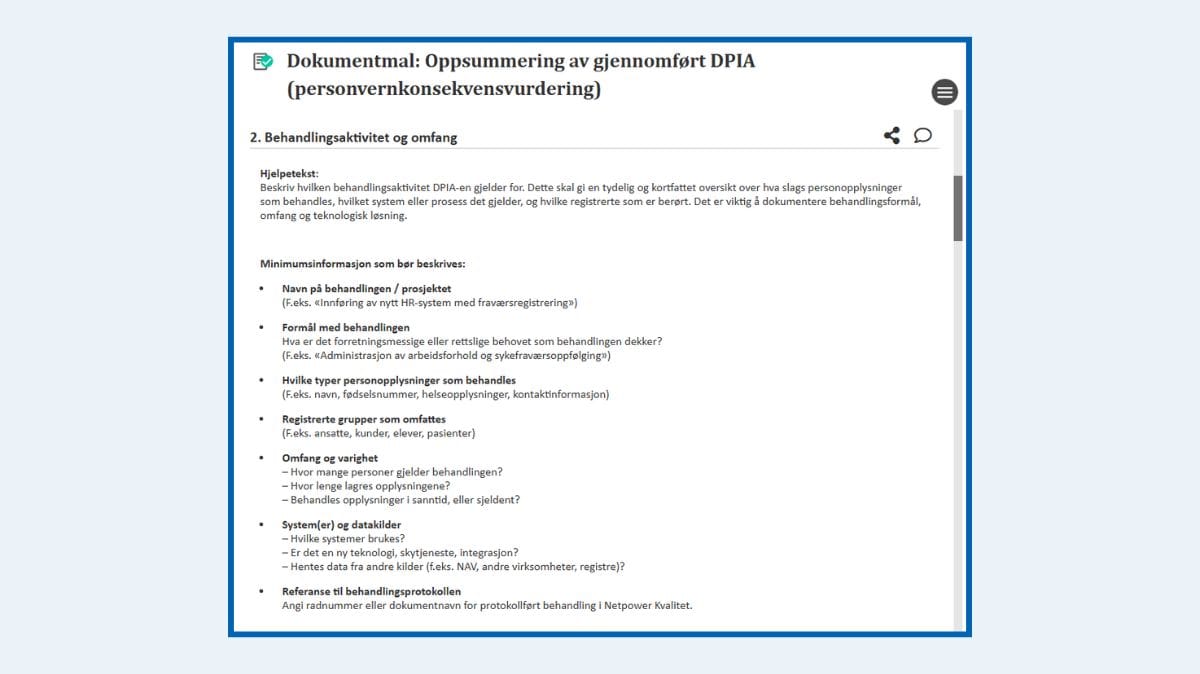
DPIA document template

Once a DPIA has been completed, the results can be documented using a dedicated DPIA template in Certain QMS. The template helps you systematically summarise the purpose, processing activity, assessed risk, actions and conclusion. Built-in guidance text and a clear structure ensure that all relevant elements are covered, even for users without specialist data protection expertise.

The document can be linked directly to the records of processing activities, and serves as the organisation’s documented evidence that the assessment has been carried out in accordance with GDPR Article 35. The DPIA documentation can be used in management reviews, internal controls or external audits, and ensures both traceability and compliance.
Dokumentmal oppsummering gjennomført DPIA Certain QMS

Document template for summarising a completed DPIA.

Systematic risk work for information security

Certain QMS offers a tool that covers the entire risk management process, from planning through to follow-up:

  • Planning
  • Risk analysis
  • Risk evaluation
  • Risk management

Within the solution, information security is configured as a dedicated risk area. The analysis is delivered with a pre-configured template that includes relevant impact areas, acceptance levels and predefined events to be assessed. The predefined event register streamlines the work for the analysis team, enabling them to focus on assessing and prioritising risks rather than starting from a blank page when identifying potential threats.

All steps and fields in the analysis include extensive guidance text to guide the user through the process. The guidance text can also be adapted to the organisation, and consequence levels are described with explanatory text to support assessments.

The risk analysis template supports:

  • Predefined events, causes and actions
  • Multiple impact areas, including CIA + data protection rights
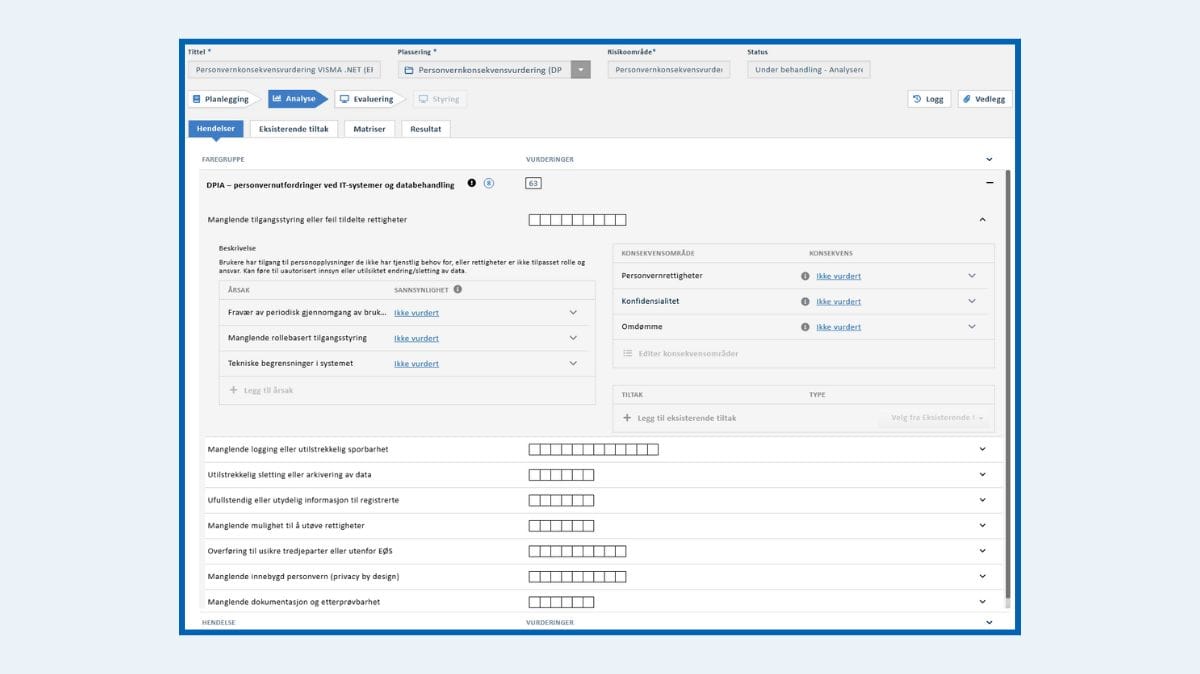
Analysemal for DPIA Certain QMS

Analysis template for DPIA.

Visual and dynamic overview of the risk landscape

Certain QMS provides a visual representation of the risk landscape through both risk matrices and table views. This makes it straightforward to understand and communicate which threats have been assessed as most critical, and which actions have been put in place.

The solution also offers a dynamic risk report where you can filter by risk area, responsible party, department and other parameters. This gives the organisation a real-time reflection of the actual risk landscape, based on which analyses have been carried out and assessed.


The report makes it possible to:

  • View aggregated risk within areas such as information security, data protection or ICT operations
  • Identify risks that lack actions or have a high residual uncertainty
  • Give management an up-to-date and documented overview of the organisation’s risk profile

This supports systematic follow-up, simplifies audits and ensures that risk work is embedded and visible across the organisation.

Risk management with actions and action plan

Once the risk analysis has been completed, an action plan is drawn up to reduce the risks associated with information security. The action plan forms the basis for risk management, with the risk owner taking responsibility for follow-up.

In Certain QMS, all of this can be handled directly within the solution, and tasks to be carried out can be assigned from the tool.

In the management phase, the risk owner can:

  • Prioritise actions for implementation
  • Accept residual risk
  • Delegate responsibility for implementing actions
  • Set deadlines for actions and follow-up
  • Record costs associated with implementation
  • Monitor the status and progress of each action

Risk management is concluded when the risk owner has assessed the effect of the actions implemented, signed off on the residual risk and formulated a final conclusion for the work.

Compliance register

A compliance register is an overview of requirements from legislation, standards and internal guidelines, linked to relevant documentation in the management system. In Certain QMS, the compliance register is one of many available features that helps the organisation maintain an overview and ensure compliance.

For ISO 27001 Annex A, all 93 controls are pre-registered in the system. Each control includes an explanation of what it entails and status fields indicating whether the requirement has been met. This makes it straightforward to use the register in audits, gap analyses and improvement work.

A ready-made template set for a GDPR article register can also be produced as part of the delivery.
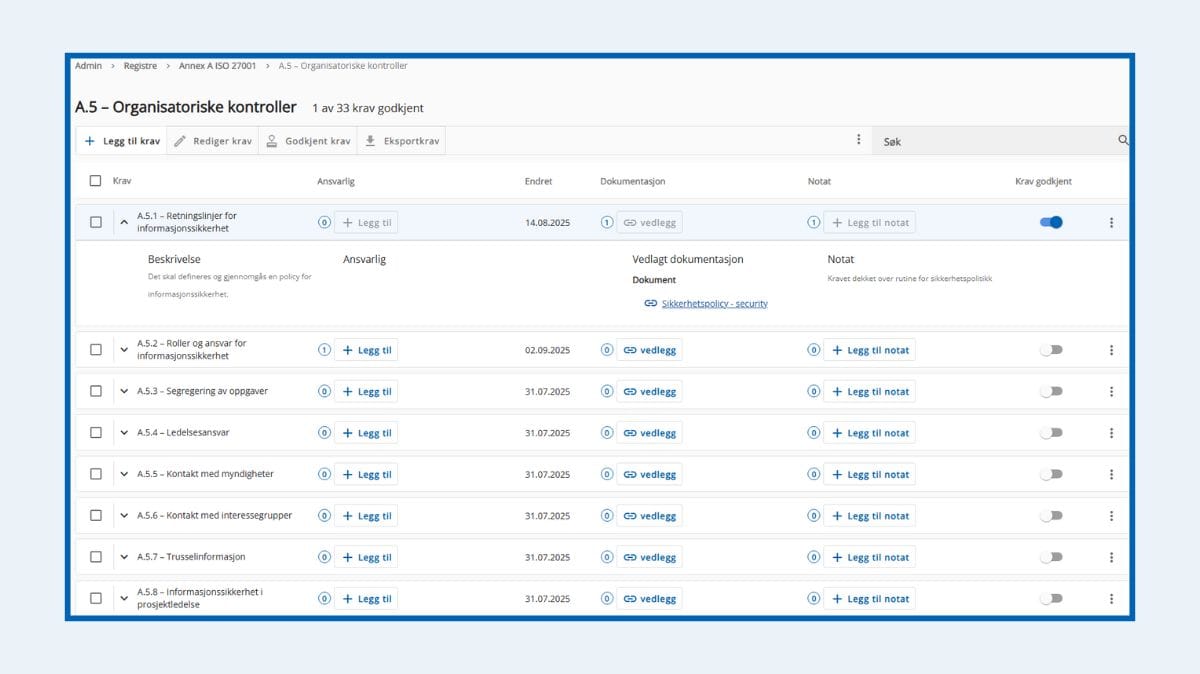
Samsvarsregistermannex A ISO 27001

Compliance register for Annex A ISO 27001.

Records of processing activities and GDPR

Certain QMS offers a table-based document template for records of processing activities that follows the requirements of GDPR Article 30 and the Norwegian Personal Data Act. The template includes fields for the legal basis for processing, types of personal data, storage, security measures and other relevant information.

The documentation can also be linked to associated DPIAs and compliance assessments, giving the organisation a clear overview of all connections between processing activities, risk and legal requirements.

Follow-up and version control

As part of the work with records of processing activities, Certain QMS also supports control of the records through the annual planner for continual improvement. Version management and availability of the records of processing activities are handled directly in the document module, so that all changes and updates can be easily followed up.

Making documentation available and sharing it

Certain QMS supports the publishing of selected documents on internal or open portals. This enables employees, customers and partners to access relevant information without having to navigate the entire system.

This supports compliance by ensuring that all relevant parties always have access to correct and up-to-date documentation. In this way, requirements for compliance, training and internal control are met, whilst important processes and routines become transparent to all who need them.
Leder som følger opp informasjonssikkerhet ISMS

ISMS package for Certain QMS

Ready to install and use from day one

Our ISMS package is delivered pre-configured and installed on the customer’s own Certain QMS installation. Each package gives the organisation everything needed to establish, document and follow up an information security management system in line with ISO 27001 and GDPR:

  • ISMS documentation: procedures, policies and process models
  • Annual planner for establishment
  • Annual planner for continual improvement
  • Risk analysis templates for information security
  • DPIA support with checklists, guidance and risk templates
  • Compliance register for ISO 27001 and the option of a GDPR article register
  • Document template for records of processing activities
  • Full version control and role-based access for all documentation

The packages are ready to use from day one, but can be adapted to the organisation’s needs and existing processes.

Contact us for a demonstration and pricing.
SharePoint as a work surface for a quality management system

SharePoint as a work surface for a quality management system

Certain QMS SharePoint

A prerequisite for succeeding with quality management and improvement is that all employees have quick and easy access to internal documentation and internal reporting systems.

That is why we have chosen to make the functions that all employees need to use available in SharePoint.

SharePoint is familiar and user-friendly

Adopting “yet another IT system” can be demanding for employees who do not have direct responsibility for developing the organisation’s QHSE processes. At the same time, the entire organisation should benefit from the QHSE work carried out within the quality management system.

With SharePoint as the work surface, employees can search for internal procedures and processes, and report non-conformances without leaving the intranet. Notifications in SharePoint and shortcuts to reading lists ensure that information reaches all employees.

Quick and easy access to up-to-date and relevant information is the key to improvement – and that is what we can offer with SharePoint as the work surface.

What can you do in SharePoint?

In SharePoint we have gathered the most important functions for the organisation’s employees, along with useful notifications for tasks that require handling directly in Certain QMS.

Non-conformances

All types of non-conformances, suggestions for improvement or reports of serious concerns can be registered by employees directly in SharePoint.

Case handlers for non-conformances and other types of cases receive notifications in SharePoint showing the status of the following:

  • Number of new cases awaiting assignment to a case handler
  • Number of own cases currently being processed
  • Number of tasks and measures not yet closed
  • Number of cases that have exceeded the internal deadline

Processes

  • Search for processes
  • Navigate the process landscape
  • Read and click on activities within processes

Employees who produce or are responsible for the organisation’s processes receive dedicated notifications showing how many processes have not been approved or have passed their revision deadline.

Documents

  • Search for documents
  • Read documents
  • Confirm reading

Employees who produce or are responsible for the organisation’s documentation receive dedicated notifications showing how many documents are awaiting approval or consultation, or have passed their revision deadline.

Reading lists

  • Display of a personalised reading list applicable to the employee’s role or position
  • Notification showing the number of unread documents in the reading list

Risk

Employees who carry out risk assessments in Certain QMS receive notifications showing the number of their own risk analyses currently in progress, and the number of risk-reducing measures that have not yet been closed.

Useful for multiple types of users

Certain QMS is a digital solution designed to be used in different ways and for different tasks, depending on the role a person holds within the organisation. For everyone with management or QHSE responsibilities, Certain QMS will be an important professional and governance system.

For employees who work directly within the system – for example, producing documentation, carrying out risk analyses or handling non-conformances – SharePoint will also be useful for notifications and status updates.

The personalised section of SharePoint displays new cases, unread documents or deadlines for revision and case handling. This gives those responsible a quick overview of tasks awaiting attention and a practical shortcut directly to the work surface in Certain QMS.

The user account in SharePoint is linked to the user account in Certain QMS, so information and access permissions will always be tailored to each individual employee and their role.

Marte Sunde

Marte Sunde

Business Consultant

Marte Sunde is a Business Consultant for Certain QMS, specialising in quality management and HSE systems. She works at the intersection of operational practice and digital solutions, helping organisations implement and improve management systems that ensure compliance, structure, and continuous improvement.

ISO 42001: The standard for AI management systems

ISO 42001: The standard for AI management systems

ISO 42001 rådgivning

ISO 42001 is the world’s first international standard for AI management systems. The standard gives organisations a framework for managing risk, accountability, transparency and continual improvement in connection with the use of artificial intelligence (AI).

As artificial intelligence becomes an increasingly important part of organisations’ work processes, requirements for control, documentation and responsible use are also growing. At the same time, the EU is introducing new regulations through the AI Act. This is driving growing interest in establishing an AI management system based on ISO 42001.

In this article, we explain what ISO 42001 is, which organisations it is relevant for, what requirements it sets out, how it relates to the AI Act and how organisations can work towards certification.

What is ISO 42001?

ISO/IEC 42001:2023 is the world’s first international standard for artificial intelligence management systems. The standard has been developed by ISO (International Organization for Standardization) and IEC (International Electrotechnical Commission) and describes the requirements for an Artificial Intelligence Management System (AIMS).

In the same way that ISO 9001 provides a framework for quality management and ISO 27001 provides a framework for information security, ISO 42001 provides a framework for the governance of artificial intelligence.

The goal is to help organisations use AI in a responsible, documented and controlled manner. The standard covers the development, procurement, implementation and use of AI systems.

ISO 42001 can be used by organisations in all industries and of all sizes, whether they develop their own AI solutions or use AI technology supplied by others.

Why was ISO 42001 developed?

AI creates significant opportunities for efficiency, innovation and better decision support. At the same time, the technology introduces new types of risk that traditional management systems do not fully address.

Organisations must, amongst other things, address questions such as:

  • How do we ensure that AI models produce reliable results?
  • How do we detect bias or discrimination in AI systems?
  • How do we document decisions that have been influenced by AI?
  • How do we safeguard data protection and information security?
  • Who is accountable if AI provides incorrect recommendations or decision support?
  • How do we monitor AI systems that evolve over time?

ISO 42001 was developed to give organisations a structured method for addressing these challenges through established management principles, risk management and continual improvement.

Certain QMS rådgivning

Who is ISO 42001 relevant for?

Many assume that ISO 42001 is only relevant for technology companies that develop their own AI models. In practice, the target audience is far broader. The standard is relevant for all organisations that develop, supply or use AI in their products, services or work processes.

    General businesses

    Organisations that use tools such as Microsoft Copilot, ChatGPT or other AI features in their day-to-day work processes.

    Healthcare and public sector

    Organisations that use AI for analysis, decision support or automation of work processes.

    Industry and manufacturing

    Companies that use AI for predictive maintenance, quality control or production optimisation.

    Finance and insurance

    Organisations that use AI for risk assessments, fraud detection or automated decision-making.

    Software companies

    Organisations that develop AI-based products or build AI functionality into existing solutions.

    Consultancy and advisory firms

    Organisations that assist clients with AI advisory services, implementation or development.

    Are you already using AI in your organisation?

    Many organisations think of AI as advanced language models or purpose-built solutions. The reality is that many organisations are already using AI today without being consciously aware of it.

    AI is becoming an integrated part of:

    • Microsoft 365
    • CRM systems
    • ERP solutions
    • Analytics and reporting tools
    • Marketing platforms
    • Customer service systems
    • Recruitment tools

    This means the need for AI governance applies not only to organisations that develop AI, but also to organisations that use AI as part of their work processes.

    What is an AI management system?

    An AI management system — also referred to as an artificial intelligence management system — is the totality of processes, roles, guidelines, controls and documentation that ensures responsible use of AI within the organisation.

    The goal is not to control the technology alone. The goal is to control how the organisation uses the technology.

    An AI management system contributes, amongst other things, to:

    • Clear roles and responsibilities
    • Systematic risk management
    • Control over data and models
    • Documentation of decisions
    • Monitoring of AI systems
    • Non-conformity handling
    • Continual improvement

    In the same way as other ISO-based management systems, the AI management system should be an integrated part of the organisation’s leadership and operations.

    How is ISO 42001 structured?

    ISO 42001 follows the same harmonised structure used in modern ISO standards. This makes it easier to integrate the standard with existing management systems such as ISO 9001 and ISO 27001.

    The requirements are organised into the following main clauses.

    Clause 4 – Organisational context

    The organisation must understand how AI affects stakeholders, business objectives and its environment.

    Clause 5 – Leadership

    Management must establish policy, responsibilities and objectives for the AI management system.

    Clause 6 – Planning

    The organisation must identify risks, opportunities and necessary actions.

    Clause 7 – Support

    Requirements for competence, resources, communication and documentation.

    Clause 8 – Operations

    Management of AI-related activities and processes.

    Clause 9 – Performance evaluation

    Monitoring, measurement, internal audit and management review.

    Clause 10 – Improvement

    Handling of non-conformities and continual improvement of the management system.

    Certain QMS rådgivning

    What requirements does ISO 42001 set out?

    Although the standard contains many detailed requirements, there are a number of central themes that recur throughout.

    AI governance

    The organisation must establish clear governance mechanisms for the use of artificial intelligence. This includes, amongst other things, roles, responsibilities, decision-making processes and reporting.

    Risk management

    AI-related risks must be identified, assessed and managed systematically. The risks may be technical, legal, ethical or commercial in nature.

    Impact assessments

    The standard places significant emphasis on understanding the consequences AI systems may have for individuals, the organisation and society.

    Lifecycle management

    AI systems must be governed throughout their entire lifecycle:

    • Planning
    • Development
    • Testing
    • Implementation
    • Operations
    • Monitoring
    • Decommissioning

    Data governance

    The organisation must maintain control over the quality, provenance and use of data employed in AI systems.

    Transparency

    Stakeholders must receive the necessary information about how AI is used and what consequences its use may have.

    Continual improvement

    The AI management system must be evaluated and improved over time in the same way as other management systems.

    We can assist with ISO 42001

    Get in touch to find out how we can help your organisation!

    Which organisations should establish an AI management system?

    There is no definitive answer, but certain organisations will have greater need than others.

    An AI management system is particularly relevant if the organisation:

    • Develops its own AI solutions
    • Delivers AI-based services to customers
    • Uses AI in decision-making processes
    • Processes personal data through AI
    • Operates in regulated industries
    • Anticipates requirements from customers or authorities relating to AI

    Many organisations are already finding that customers are asking questions about how AI is used, which data is employed and which controls are in place.

    Certain QMS rådgivning

    How does ISO 42001 differ from ISO 9001?

    ISO 9001 is about quality management.

    ISO 42001 is about the governance of artificial intelligence.

    Both standards are built on risk-based thinking, management commitment and continual improvement. ISO 42001, however, introduces requirements that are specific to AI.

    These include, amongst others:

    • AI risk assessments
    • Data governance
    • Transparency
    • Human oversight
    • Impact assessments
    • AI-specific governance

    For organisations already certified to ISO 9001, much of the structure will be familiar.

    How does ISO 42001 differ from ISO 27001?

    ISO 27001 focuses on information security.

    ISO 42001 focuses on the governance of artificial intelligence.

    There is significant overlap between the standards, particularly in:

    • Risk management
    • Supplier management
    • Documentation
    • Internal audit
    • Management review
    • Continual improvement

    Many organisations will therefore be able to integrate ISO 42001 with existing management systems based on ISO 27001.

    What is the difference between ISO 42001 and AI governance?

    AI governance describes the discipline or field concerned with the management of artificial intelligence.

    ISO 42001 is a concrete standard that describes how organisations can establish a management system for AI governance.

    One way to put it is:

    • AI governance is the goal.
    • ISO 42001 is the framework.

      In the same way that information security is the field, whilst ISO 27001 is the standard that describes how the work can be organised.

      How does ISO 42001 relate to the EU AI Act?

      The AI Act is the EU’s regulatory framework for artificial intelligence.

      ISO 42001 is an international standard for AI management systems.

      These are two different things, but they share many common themes.

      The AI Act sets legal requirements for certain types of AI systems. ISO 42001 provides a governance framework that can help organisations establish the processes, responsibilities and documentation that support compliance with these requirements.

      Both focus, amongst other things, on:

      • Risk management
      • Documentation
      • Transparency
      • Accountability
      • Monitoring
      • Human oversight

      Can ISO 42001 help the organisation with the AI Act?

      Yes. ISO 42001 is an international standard and can be certified through accredited certification bodies in the same way as ISO 9001 and ISO 27001.

      Interest in ISO 42001 is still at an early stage, but many expect demand to increase significantly as the AI Act gains greater relevance and AI is adopted by a growing number of organisations.

      How does an organisation become certified to ISO 42001?

      The path to certification will vary between organisations, but typically involves the following steps:

      1. Map current AI use

      Identify which AI systems are in use within the organisation.

      2. Carry out a gap analysis

      Compare current practice against the requirements of ISO 42001.

      3. Establish an AI management system

      Define roles, responsibilities, processes and the necessary documentation.

      4. Implement the necessary controls

      Carry out actions relating to risk management, data governance and governance.

      5. Carry out an internal audit

      Verify that the management system is functioning as planned.

      6. Carry out a management review

      Management must evaluate the system’s effectiveness and maturity.

      7. Certification audit

      An accredited certification body carries out an audit and assesses whether the requirements have been met.

      How to get started with ISO 42001

      For many organisations, the most important first step is to gain an overview.

      Start by mapping:

      • Which AI tools are in use within the organisation
      • Who is using them
      • Which data is being processed
      • Which risks exist
      • Which requirements customers or authorities are setting

      The organisation can then establish a management system that builds on existing processes for quality, information security, data protection and risk management.

      Certain QMS rådgivning

      Advisory services and support on the path to certification

      ISO 42001 is the world’s first international standard for AI management systems. The standard gives organisations a structured framework for managing risk, accountability, transparency and continual improvement in connection with the use of artificial intelligence.

      As AI becomes an increasingly important part of how organisations work, make decisions and deliver services, the need for AI governance and documented management will grow.

      For organisations wishing to establish an AI management system, prepare for the AI Act or document maturity in the responsible use of artificial intelligence, ISO 42001 is likely to become one of the most important standards in the years ahead.

      Summary

      ISO 42001 is the world’s first international standard for AI management systems. The standard gives organisations a structured framework for managing risk, accountability, transparency and continual improvement in connection with the use of artificial intelligence.

      As AI becomes an increasingly important part of how organisations work, make decisions and deliver services, the need for AI governance and documented management will grow.

      For organisations wishing to establish an AI management system, prepare for the AI Act or document maturity in the responsible use of artificial intelligence, ISO 42001 is likely to become one of the most important standards in the years ahead.

      Talk to us about AI management systems

      We help organisations with advisory services, establishment and further development of AI management systems. Get in touch to find out how we can help you!

      Mirjam Meling

      Mirjam Meling

      Marketing & Communication Manager

      Produces content for Certain QMS on management systems, quality management, information security and AI governance. She works with subject matter experts to communicate complex topics in a clear and practical way.

      The AI Act: who faces new requirements, and who is largely unaffected?

      The AI Act: who faces new requirements, and who is largely unaffected?

      The AI Act and Norwegian organisations

      When the General Data Protection Regulation (GDPR) was introduced, virtually every organisation was affected. Many leaders are therefore asking whether the AI Act will have similar consequences. The answer is more nuanced.

      The AI Act is built around a risk-based approach, where the requirements depend on how artificial intelligence is used and what consequences it may have for individuals and society. Two organisations can therefore use AI every day whilst facing entirely different regulatory requirements.

      For most organisations, it is not the industry alone that determines how significantly they are affected by the AI Act. What matters is which AI systems are in use, which data they process, and whether they feed into decisions that affect individuals.

      The AI Act does not regulate all uses of artificial intelligence equally

      The AI Act distinguishes between different risk levels. Whilst certain types of AI are prohibited, the most stringent requirements will apply to what are known as high-risk systems.

      This means that many organisations will be able to use generative AI tools without extensive new obligations, whilst others must establish documented processes for risk assessment, control and follow-up.

      It is therefore misleading to ask whether an organisation is “covered by the AI Act”. Every organisation that uses AI will be affected to a greater or lesser degree. The key question is how significant the regulation will be for each individual organisation.

      Organisations with limited impact

      For many organisations, AI is used primarily as a tool that supports employees in their day-to-day work.

      Examples include:

      • Generating text drafts and content
      • Summarising meetings and documents
      • Coding assistance for developers
      • Language support and translation
      • Analysis of large volumes of information

      In such cases, it is humans who make the decisions, whilst AI functions as a productivity tool.

      Although these organisations should still maintain an overview of which AI solutions are in use, they will not normally face the most extensive requirements under the AI Act.

      Organisations with moderate impact

      A different picture emerges when AI becomes an integrated part of operational processes.

      In industry, energy, transport and offshore, artificial intelligence is increasingly used for analysis, optimisation and predictive maintenance. AI can help identify anomalies, predict failures or recommend actions based on large volumes of data.

      In such cases, the primary challenge is not necessarily human rights or discrimination. Rather, the need for control over data quality, traceability and an understanding of how AI models influence the basis for decisions becomes more pressing.

      Many organisations in these sectors will therefore find that the AI Act creates a need for better documentation and governance, even if the solutions are not necessarily classified as high-risk systems.

      Organisations that may be subject to stricter requirements

      The most extensive requirements under the AI Act are linked to AI systems that can affect individuals’ rights, opportunities or access to essential services. This applies, amongst others, to solutions used in the following areas.

      Recruitment and HR

      AI used to rank candidates, filter applications or make recommendations in recruitment processes may fall within the high-risk categories of the regulation.

      Education

      AI solutions that affect the assessment of students or decisions about educational pathways may trigger stricter requirements.

      Healthcare and social care

      AI used for diagnostics or clinical decision support is among the areas subject to significant regulation.

      Public sector

      Municipalities, directorates and other public bodies must be particularly attentive if AI is involved in case processing or decisions that affect citizens.

      In such cases, the AI Act sets requirements for, amongst other things, risk management, documentation, human oversight and ongoing follow-up.

      AI Act readiness is about the organisation’s AI portfolio

      For leaders, it is therefore more relevant to map the organisation’s AI portfolio than to attempt to determine whether the organisation “is covered by the AI Act”.

      Two organisations in the same industry can have very different risk profiles.

      A university using AI for administrative tasks faces different requirements from one using AI to assess students. In the same way, a municipality using generative AI for content production will have a different risk profile from one using AI in case processing or decision-making.

      The first step towards AI Act readiness is therefore to establish an overview of which AI systems are in use within the organisation, which processes they form part of, and what the consequences could be if they produce incorrect results.

      From AI use to AI governance

      For many organisations, the AI Act will not entail extensive new requirements in the near term. Nevertheless, the regulation helps to make visible a need that already exists: the need for control over how artificial intelligence is used within the organisation.

      Organisations that establish an early overview of their AI portfolio will be better placed to handle both regulatory requirements and the rapid development of artificial intelligence.

      Talk to us about AI management systems

      We help organisations with advisory services, establishment and further development of AI management systems. Get in touch to find out how we can help you!

      Mirjam Meling

      Mirjam Meling

      Marketing & Communication Manager

      Produces content for Certain QMS on management systems, quality management, information security and AI governance. She works with subject matter experts to communicate complex topics in a clear and practical way.

      AI risk management is not like other risk – this is how ISO 42001 approaches it

      AI risk management is not like other risk – this is how ISO 42001 approaches it

      AI risiko

      Many organisations already have established risk management processes. They identify risks, assess likelihood and impact, implement actions and follow up through audits and management reviews.

      But artificial intelligence challenges several of the assumptions that traditional risk management is built on.

      It is precisely for this reason that ISO 42001 places such emphasis on AI risk management. The standard builds on familiar principles from management systems, but also acknowledges that AI introduces risk factors that many organisations have not previously had to manage.

      Why is AI risk different?

      Traditional IT systems generally do what they are programmed to do. If a rule or process is defined, the system will follow it.

      AI systems work differently.

      They are typically built on statistical models that learn patterns from large volumes of data. The result is that the outcome is not always as predictable as in traditional software. The system can produce different answers to the same question, change behaviour over time or draw conclusions that are difficult to explain fully.

      This does not mean that AI is necessarily dangerous. But it does mean that the risk must be assessed differently.

      Risk is not only about technology

      When leaders think about technology risk, it tends to focus on availability, security and data protection.

      For AI, these remain important, but the risk landscape is broader.

      Organisations must also consider questions such as:

      • Can the AI model produce incorrect or misleading responses?
      • Can it introduce bias or discrimination?
      • Could employees become overly reliant on AI-generated recommendations?
      • Is it clear who is accountable when AI is used in decision-making processes?
      • Can the system be used in ways it was not originally intended for?

      These are risks that often affect people, business processes, reputation and regulatory compliance at least as much as the technology itself.

      AI risikostyring

      AI risk is dynamic

      Another important difference is that AI risk is rarely static.

      A machine on the factory floor works much the same way tomorrow as it did yesterday. Many AI solutions, on the other hand, evolve continuously.

      Underlying data changes. Suppliers update models. New use cases emerge. Employees begin using tools in ways that differ from what was originally planned.

      ISO 42001 therefore emphasises continuous monitoring and evaluation, not just a one-off assessment before the system is deployed.

      Risk management becomes an ongoing activity.

      Focus on context and use

      A central principle in ISO 42001 is that risk lies not only in the technology, but in how the technology is used.

      The same AI model can represent very different levels of risk depending on its purpose.

      A chatbot that helps employees draft emails presents an entirely different risk profile from a system used as decision support in recruitment, credit assessment or healthcare.

      This means that effective AI risk management requires the organisation to understand:

      • Where AI is used
      • Who is affected by its use
      • Which decisions AI influences
      • What the consequences of errors could be

      This perspective runs throughout the whole of ISO 42001.

      Human oversight remains essential

      A recurring theme in the standard is the importance of human oversight.

      Many organisations introduce AI to streamline work processes, but streamlining must not lead to accountability becoming unclear.

      Leaders must be able to answer questions such as:

      • Who owns the process?
      • Who approves the results?
      • Who is accountable if something goes wrong?

      ISO 42001 therefore requires the organisation to define roles, responsibilities and decision-making authority in connection with the use of AI.

      Technology can support people. It does not relieve the organisation of responsibility.

      From technology project to governance responsibility

      One of the most common mistakes organisations make is treating AI as a purely IT project.

      ISO 42001 takes a different view.

      The standard places AI within the organisation’s existing governance model. AI should be assessed in the same way as other matters that affect the organisation’s objectives, risk exposure, compliance and reputation.

      An AI management system therefore often involves functions beyond IT alone:

      • Leadership
      • Professional departments
      • Compliance and quality
      • Data protection and information security
      • HR
      • Risk management

      The goal is not to control the technology itself, but to govern how the organisation uses it.

      Risiko med AI

      What does this mean for leaders?

      For leaders already working with quality, internal control, information security or compliance, much of the thinking in ISO 42001 will feel familiar.

      What is new is not necessarily the methodology.

      What is new is that AI introduces risks that require different assessments from those applied to traditional systems and processes — and that systematic AI risk management therefore becomes a core competence for organisations in the years ahead.

      Organisations that succeed with AI in the coming years will likely be those that manage to combine innovation with governance. Not because regulation demands it, but because trust, accountability and control become ever more important as artificial intelligence is adopted in business-critical processes.

      Talk to us about AI management systems

      We help organisations with advisory services, establishment and further development of AI management systems. Get in touch to find out how we can help you!

      Mirjam Meling

      Mirjam Meling

      Marketing & Communication Manager

      Produces content for Certain QMS on management systems, quality management, information security and AI governance. She works with subject matter experts to communicate complex topics in a clear and practical way.